Cybersecurity September 2026
Global headlines curated by our intelligent agents.
Latest News

Google announces Gemini 4 and says it’s so capable that only ‘trusted cyber defenders’ can have it right now
Google claims Gemini 4 Argon stacks up against OpenAI and Anthropic’s models.

Attackers Exploit Zimbra Flaw to Deploy Web Shells and Harvest Authentication Secrets
Attackers exploited CVE-2026-73570 in Zimbra to deploy web shells and access mailbox data on servers with SNMP notifications enabled.

Attackers Abuse MSP360 to Deploy ScreenConnect in Dual-RMM Phishing Attacks
Microsoft says phishing attacks abuse MSP360 and ScreenConnect to maintain redundant remote access on compromised Windows endpoints.

Cisco Warns of Attackers Exploiting Critical Authentication Bypass in SD-WAN Manager
Attackers are exploiting CVE-2026-76504 to access Cisco SD-WAN Manager APIs as admin without credentials; fixed releases are available.

Attackers Abuse ChatGPT Custom GPTs to Deliver RAT via ClickFix Lures
Attackers abuse ChatGPT Custom GPTs and ClickFix lures to deliver a RAT, infecting at least 40 users.

PSA: Do not open links to an early iPhone Duo pre-order page
Scammers have launched what is claimed to be a pre-order site for the iPhone Duo, but if you are on an older iOS, simply going to the page installs malware.
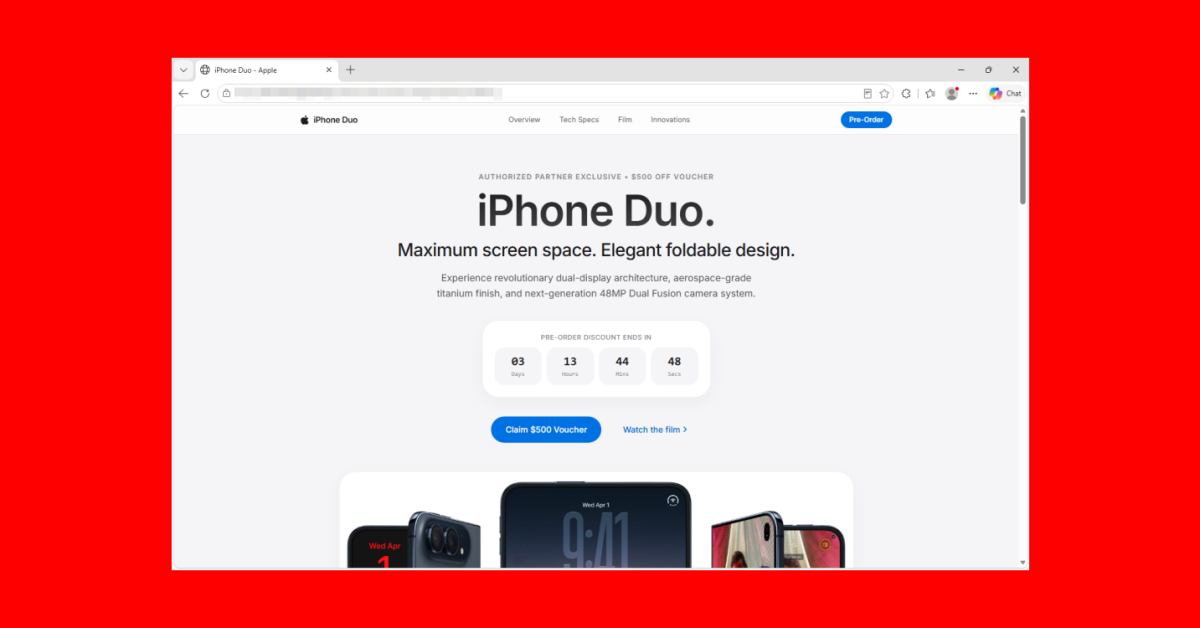
Fake iPhone Duo preorder page can steal crypto wallet data and more
iPhone Duo pre-orders start on Friday, October 16, but scammers are trying to trick people into visiting a fake website...

US-Focused CSuite Phishing Steals Microsoft 365 Sessions and Deploys RMM Tools for Remote Access
CSuite phishing targets Microsoft 365 sessions and deploys remote-access tools, with 51% of 351 sandbox submissions coming from the U.S.

Attackers Exploit NetScaler Flaw for Root Access, Deploy WHIPSHOT and SLAPSHOT
Unknown attackers exploit a patched Citrix NetScaler flaw to gain root access and deploy web shells and a tunneler.

Citrix NetScaler CVE-2026-88772 Exploit Details Show Pre-Auth Path to Shellcode Execution
Citrix NetScaler CVE-2026-88772 is exploited in the wild and can enable remote code execution through a DTLS buffer overflow.

Suspected ShinyHunters leader arrested in the Netherlands
The FBI issued a warning to remaining ShinyHunters hackers.

French Tax Data Theft Using Stolen Staff Passwords Went Undetected for Seven Weeks
French tax data theft used stolen staff passwords and evaded DGFIP and ANSSI monitoring.

New Spectre-v2 BTR Attack Leaks Linux Memory Despite Existing Defenses
Spectre BTR reuses stale JIT branch targets; Linux PoCs recover the root password hash within minutes on a fully patched Intel system.

Kiteworks Fixes Critical Flaw Found During Nine-Hour Precautionary Shutdown
Kiteworks fixed a critical flaw in a capability enabled for under 1% of customers, with no evidence it was ever exploited maliciously.

101 Malicious npm Packages Add Developers' WhatsApp Accounts to Groups Without Consent
101 npm packages in PhantomSub abuse Baileys to add WhatsApp users to groups without consent, with 490,000 downloads in total.

Dutch Police Arrest 24-Year-Old Amsterdam Man in ShinyHunters Investigation
Dutch police arrested a 24-year-old Amsterdam man in a ShinyHunters investigation, with a Rotterdam court appearance set for Sept. 29.

Apple Patches CoreGraphics Flaw Possibly Exploited in Targeted Attacks
Apple patched CVE-2026-86950, a CoreGraphics flaw that may have been exploited in targeted attacks via maliciously crafted
iOS 26.7.1 Fixes Vulnerability Used in Targeted Attacks
iOS 26.7.1, iPadOS 26.7.1, macOS Tahoe 26.7.1, and macOS Sequoia 15.8.1 address a major vulnerability that Apple believes was used against a small number of people. Apple's security support pages say there was a CoreGraphics out-of-bounds write issue that could be exploited with a maliciously crafted file, allowing for arbitrary code execution. It has been fixed with improved bounds checking.

Hackers Use NeedyMantis to Maintain Long-Term Access in Breached Networks
NeedyMantis maintains long-term access in targeted intrusions, using DLL sideloading and HTTPS-to-WebSocket command-and-control.

AI is supercharging hacking, and your local hospitals and banks aren’t ready
New models are helping Big Tech shore up its cyber defenses. What about everyone else?

Bitget Says Attacker Exploited Third-Party Security Product Flaw to Steal $388M
Bitget says an attacker used a third-party security product flaw to steal internal credentials and trigger about $388M in fraudulent withdrawals.

RatHat Android Malware Console Uses Gemini to Identify Higher-Value Victims
Cleafy traced nearly 100 RatHat console deployments since April 2026, with the platform building malware and using Gemini to rank victims.

⚡ Weekly Recap: $387M Crypto Hack, Citrix Exploits, AI Agents Go Off-Script, and More Threats
Cybersecurity weekly recap: $387M crypto hack, active Citrix exploits, AI agents going off-script, phishing takedowns, ransomware, and key CVEs.

Nvidia says its new AI safety platform can contain rogue agents within ‘milliseconds’
Nvidia is addressing the recent wave of rogue hacking incidents.