Cybersecurity News
Global headlines curated by our intelligent agents.
Latest News

Google Pauses OSS Product Bug Bounty Rewards After Surge in Invalid Automated Reports
Google temporarily stops OSS VRP product vulnerability reports after a surge in automated submissions, most of which it says are invalid.

Critical Atlassian Flaw Lets Unauthenticated Attackers Read Known Files Across 8 Products
Atlassian fixes a critical path traversal in 8 Data Center products that lets unauthenticated attackers read files if exact paths are known.

FBI Removes Accenture Contractor After Patch Failure Led to ShinyHunters Breach
FBI says a contractor failed to apply a security patch before a ShinyHunters breach stole personal details of thousands of employees.

Wikipedia operator says OpenAI’s ‘rogue’ bots may be linked to a May outage
More instances of unexpected AI bot behavior.

Microsoft Exchange Flaw Lets Authenticated Attackers Read Other Users' Mailboxes
Microsoft patches CVE-2026-96940, which lets authenticated attackers read other users' Exchange mailboxes within the same organization.

⚡ Weekly Recap: NetScaler and FortiMail 0-Days, AI Coding Leaks, Spectre v2 and Ransomware Arrests
Catch up on this week’s biggest cyber threats, including exploited zero-days, AI-related data leaks, Spectre attacks, phishing tricks, and ransomware

Realtek Jungle SDK Exploit Attempts Deliver Cling Botnet With STUN-Based C2
Realtek Jungle SDK exploit attempts deliver Cling botnet in some attacks.

Mac Users Reclaim Storage With New Apple Intelligence Removal Tool
A new open-source tool is making waves in the Mac community by helping users reclaim valuable storage space taken up by Apple's AI models. Called "RemoveMacAI," the tool disables Apple Intelligence on macOS 27, removes its downloaded models, and prevents them from being downloaded again. In macOS 27, Apple removed the toggle to disable Apple Intelligence wholesale, and simply disabling individual features doesn't remove the models from your Mac's drive.

Attackers Target Rejetto HFS Flaw That Enables Admin Session Forgery and RCE
Rejetto HFS CVE-2026-61500 faces exploitation attempts after a public PoC showed forged admin sessions can lead to remote code execution.

New NetScaler Zero-Day Exploited in Targeted Attacks Can Knock SAML Deployments Offline
Citrix patches CVE-2026-88779 after targeted zero-day attacks caused denial-of-service on SAML-enabled NetScaler deployments.

China-Aligned TA419 Targets U.S. AI Policy Experts With Microsoft AitM Phishing
TA419 targets U.S. AI policy experts with reply-triggered AitM phishing that captures Microsoft credentials and session cookies.

Warlock Exploits SharePoint Flaws to Disable Security Tools and Deploy Ransomware
Warlock exploited SharePoint flaws in attacks on at least four organizations, including two critical infrastructure operators.

The State of Cybersecurity in 2026: Key Segments, Insights, and Innovations
Cybersecurity teams are shifting toward continuous control across identity, cloud, endpoints, telemetry, and human risk.

Dell CSM Flaws Enable Unauthenticated Admin Access and Root on Kubernetes Nodes
Dell fixes six CSM flaws enabling authentication bypass, storage credential access, and cluster-wide privilege escalation.

Why CISOs Struggle to Answer the Board's Three Hardest Questions, and How to Fix the Report
Exposure-based board reporting maps attack paths across security tools and ties critical assets to financial risk and quarterly trends.

Android 17 Advanced Protection Locks Accessibility Services to Verified Accessibility Tools
Android 17 limits accessibility service access under Advanced Protection to verified Accessibility Tools, blocking a major malware abuse path.

Critical FortiMail Zero-Day Flaw Exploited in Attacks Allows Unauthenticated Arbitrary File Writes
Fortinet says attackers are exploiting a FortiMail flaw that lets unauthenticated users write arbitrary files via crafted HTTP requests.

Police Arrest 16-Year-Old Suspected of Running KillSec, Seize Ransomware Leak Site and Servers
European police arrested three KillSec suspects, seized its leak site and servers, and secured at least 110 TB of data.

ThreatsDay: AI-Powered Zero-Day Chain, 543K Live Secrets, Model Inspection RCE and 13 More Stories
This week in cybersecurity: AI-driven attacks, exposed secrets, old flaws, new exploit tricks, malware techniques, and security research worth knowing

WordPress Backdoor Rebuilds Itself After Cleanup Using Files, Database, and Shared Memory
SC WordPress malware rebuilds its backdoor from files, the database, and shared memory; fewer than 20 wpForo exploit attempts were seen since July 3.
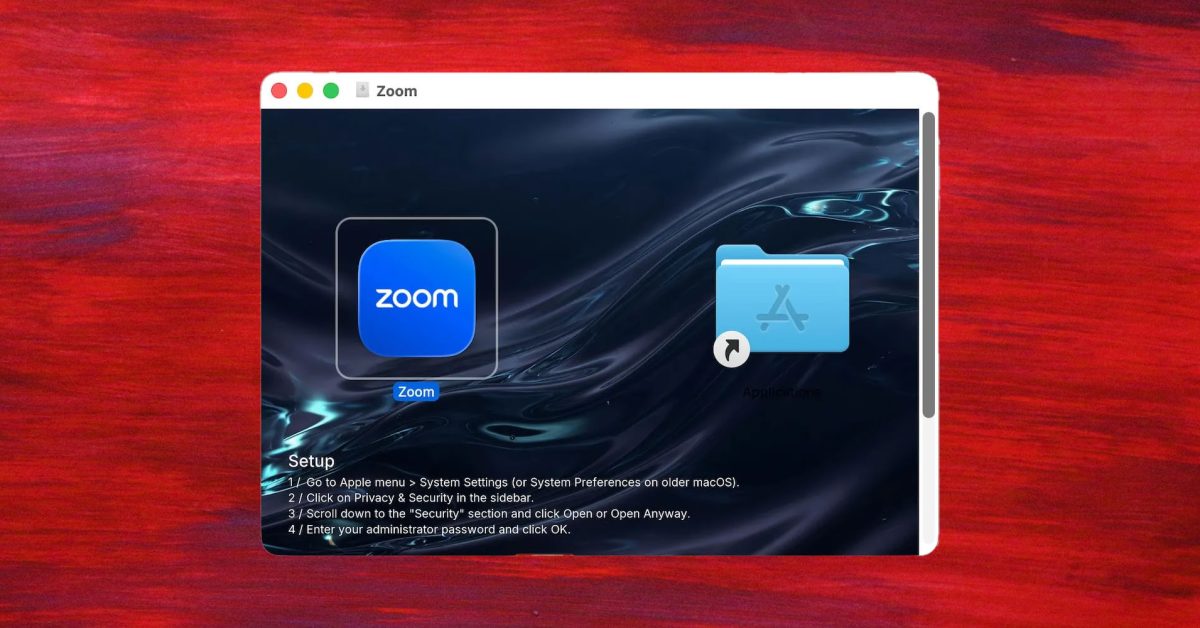
This fake Mac Zoom installer has a sneaky way to bypass Gatekeeper
Cybersecurity company Jamf has discovered a fake Mac installer for the videoconferencing app Zoom that uses a sneaky way to...

Oppo can't get accusations of Apple Watch trade secret theft dismissed
A federal judge didn't buy Oppo's OpenAI-like arguments about IP theft by an engineer that allegedly took Apple Watch trade secrets to Oppo.

CISA Adds Exploited Cisco Catalyst SD-WAN Manager Auth Bypass to KEV
Cisco confirms active exploitation of a Catalyst SD-WAN Manager authentication bypass that can grant unauthenticated attackers admin API access.
A real ChatGPT page is being used to trick people into installing malware
Attackers are using ChatGPT, Google Sites, and a fake Cloudflare check to make a malware campaign look far more convincing.